
This summary is not available. Please
click here to view the post.
Showing posts with label privacy. Show all posts
Showing posts with label privacy. Show all posts
By Olga Symeonoglou
On October 6, the European Court of Justice invalidated the Safe
Harbor pact, ruling
that the privacy rights of European citizens are being violated by American
companies. For fifteen years, the safe harbor agreement allowed U.S. companies
to transfer data of European citizens overseas, but the ECJ found that this violated
Europeans’ privacy rights because the U.S. government would have access to
their personal information. The ruling comes as a shock to many companies that
have relied on the data transfer agreement, but a new
agreement is in the works.
By Matt Klinger

The prospect of developing an international data privacy
regime seems low. But as Markus Heyder of the Center for Information
Policy Leadership writes, promoting interoperability between existing
national or regional standards may offer a practical near-term alternative.
"The basic idea behind interoperability," he writes "is
that different privacy regimes can be made to work together through negotiated
codes of conduct or similar schemes."
Heyder cites a recent publication by European Union authorities that
seeks to help businesses simultaneously meet the privacy requirements of the
E.U. and Asia-Pacific Economic Cooperation region. Heyder notes this
effort may stimulate similar initiatives elsewhere.
By Matt Klinger
Recent moves by Asian governments show that privacy protection is not just a concern in the United States. and European Union.
For instance, just this month Japan issued a voluntary code of practice for businesses that collect and use personal data. In addition, earlier this year, Vietnam created new sanctions for certain violations involving data privacy, while the government of Hong Kong issued a best practices guide for developing a privacy management program.
Recent moves by Asian governments show that privacy protection is not just a concern in the United States. and European Union.
For instance, just this month Japan issued a voluntary code of practice for businesses that collect and use personal data. In addition, earlier this year, Vietnam created new sanctions for certain violations involving data privacy, while the government of Hong Kong issued a best practices guide for developing a privacy management program.
These efforts add further complexity to the patchwork of
privacy regulations and best practices companies should follow when operating
in Asia.
By Matt Klinger
In late February, Isabelle
Falque-Pierrotin was elected to serve as the new chairwoman of the European
Union's Article 29 Working Party, a group that plays an advisory
role on data protection issues to both the European Commission and to the E.U.
member states.
Falque-Pierrotin will face two major challenges in
her new role: transitioning the E.U. to a new data protection regulation
that likely will be implemented in the coming months and promoting
international cooperation between data protection authorities.
In
addition to serving a two year term as head of the Working Party, Falque-Pierrotin will continue to serve as the Chairwoman of the French Data
Protection Authority (CNIL), a post she has held since 2011.
Earlier this
year the CNIL handed down its highest financial penalty ever when it
sanctioned Google 150,000 euros for violating several provisions of the French
Data Protection Act.
By Matt Klinger

To prevent surveillance by the National Security Agency
(N.S.A), some large companies with customers outside the U.S. are offering to
store their client's data entirely abroad.
Microsoft, for instance, recently indicated it would give customers some choice
about where their data is stored. Similarly, a Dutch telecom operator plans to set up servers in the
Netherlands so that its encrypted data never leaves the country, while an alliance of German phone and internet operators have
discussed doing a similar thing. Going even a step further, Brazil has considered legislation that would force companies
like Facebook to store data on Brazilian users inside the country. And some European Union (E.U.) officials support
requiring E.U. citizens' data to be stored within the union's borders.
But how effective are such measures likely to be? Not
very, according to some analysts, including a retired deputy director of the N.S.A. It seems
foreign countries that want to protect their citizens' data will have to
benefit from legal reforms, such as changes to U.S. law or the adoption of a
binding international instrument. But such measures are unlikely to take
effect soon, if at all.
By Matt Klinger
The International Association of Privacy Professionals
(IAPP) is holding its annual Global Privacy Summit March 5-7 in Washington, D.C.
The event, which last year had over 1,000 attendees, includes discussions
on all the most important, and contentious, privacy issues and speakers from
across the globe. This year's panelists include senior regulatory
officials, chief privacy officers of major corporations, and, of course,
lawyers from academia and private practice. The summit also provides an
opportunity to study and test for the IAPP's suite of professional
certifications in privacy.
By Matt Klinger
In late January, the Federal Trade Commission (FTC) announced settlements with three professional football
teams, a large internet service provider, and eight other companies over
charges they falsely claimed compliance with a framework that allows the
transfer of personal data from the European Union to the United States.
To comply with the
framework, known as Safe Harbor, an organization must annually self-certify to
the U.S Department of Commerce that it meets certain privacy protection
requirements. But organizations that let their certification lapse, as
some in the settlement agreement did, can no longer claim compliance.
Some observers question whether the announcement is an effort to
mollify E.U. officials who have recently questioned the effectiveness of Safe
Harbor. No matter the impetus, the FTC has made its commitment to
enforcing Safe Harbor clear, and certified organizations should remain vigilant
about their status.
By Matt Klinger
Last month the European Court of Human Rights (ECHR) fast-tracked a case filed by a London-based activist
groups against the U.K. government for its alleged involvement in the U.S.
National Security Agency's PRISM surveillance program.
The groups filed
their complaint with the ECHR in September, alleging the
U.K. intelligence services participating in PRISM were violating Article 8 of
the European Convention on Human Rights. In particular, Article 8 requires that any government interference in an individual's private or family
life must be "in accordance with the law" and "necessary in a democratic
society." The U.K. government now has until May 2nd to respond to
several questions from the court.
Axel Arnbak at Freedom to Tinker has insightfully analyzed how the court
is likely to approach the case.
By Matt Klinger
"The
first major statement by the UN on privacy in 25 years" appeared last
month when the General Assembly's committee on humanitarian issues unanimously
approved a resolution on "the
right to privacy in the digital age."
Brazil and Germany, which
recently learned the U.S. National Security Agency had intercepted the
communications of their top leaders, sponsored the non-binding measure.
The resolution calls on member states to review their legislation and
practices regarding communications surveillance with an eye toward upholding
the right to privacy. The resolution also calls for a U.N. report on the protection
and promotion of privacy in the context of "domestic and extraterritorial
surveillance . . . including on a mass scale."
The committee's
consensus approval indicates the resolution will easily pass in the General
Assembly when it comes up for a vote this December.
By Peter Andres*
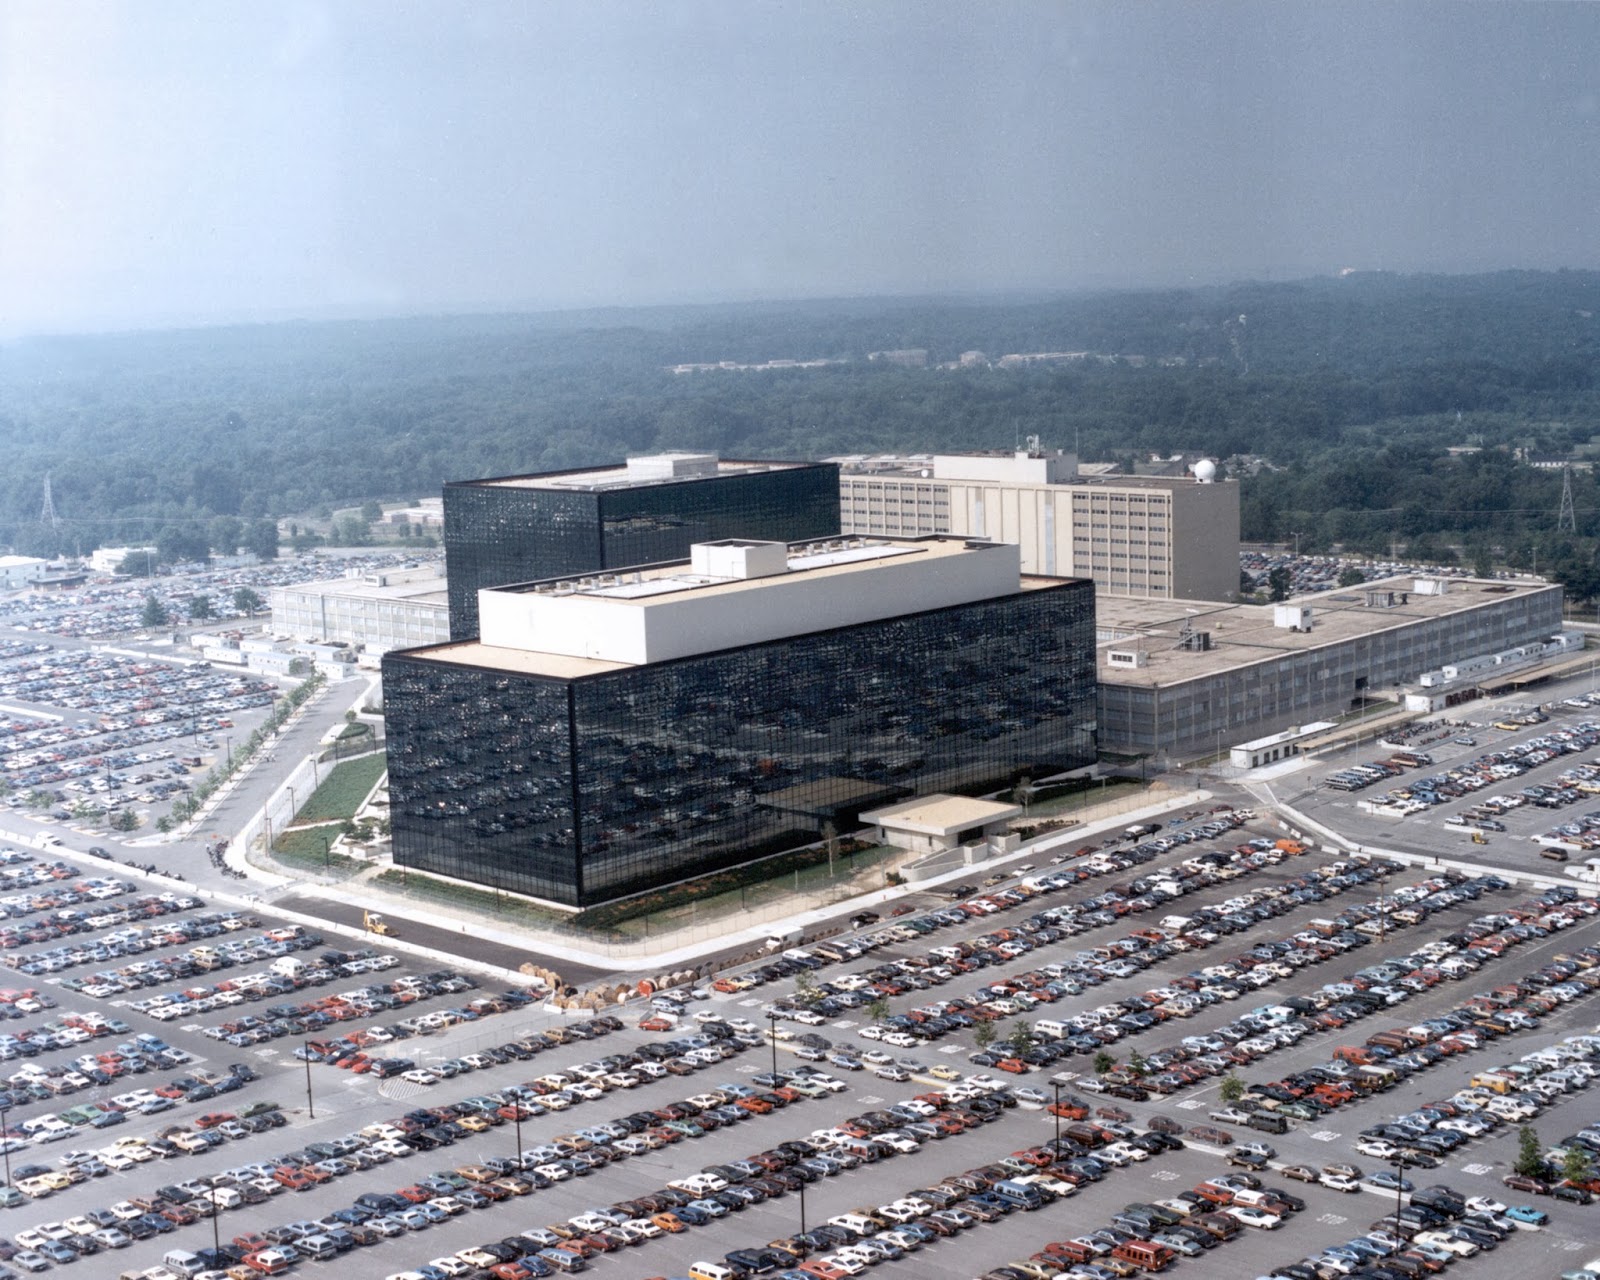 |
| The National Security Agency at Fort Meade | Photo courtesy of the Department of Defense |
Since May 2013, each month we have learned a little more
about the trove of
documents that Edward Snowden took from the National Security Agency (NSA).
And with each revelation the scope of the U.S. spying program continues to
grow. To date, public
opinion appears to be split between those that casually brush off the
spying with a “what do I have to hide?” attitude, while others finds the
revelations a much more insidious invasion of privacy.
For lawyers working on matters with international clients
based outside of the United States, the Snowden revelations raise practical issues
that impact their practice given the scrutiny international communications
receive under NSA surveillance programs.
As a Washington
Post article noted in October, “intercepting communications overseas has
clear advantages for the NSA … [bulk] collection of Internet content would be
illegal in the United States, but the operations take place overseas, where the
NSA is allowed to presume that anyone using a foreign data link is a foreigner.” The Snowden disclosure has particular
resonance for attorney communication with non-U.S. citizen clients, who still
may be subject to U.S. jurisdiction. If
a confidential communication is sent to a Gmail account or another U.S. e-mail service
provider and sent to a data center in Asia, should it be assumed that the NSA
has access to it?
By Matt Klinger
In October, the European Commission's official data
protection advisory group, the Article 29 Working Party, issued its
latest guidance for complying with the EU's e-Privacy Directive
(affectionately known as the "Cookie Directive").
Among other
provisions the new guidance provides that when accessing a website, users must
have access to "all necessary information" about the types and
purposes of cookies used by the site. In addition, the guidance clarifies
that a user's consent to place cookies on a device, which is required by the
Cookie Directive, must be sought before cookies are set or read.
Meanwhile, the Wall Street Journal reports that Google, Microsoft, and Facebook are each
developing online tracking methods that could eventually make cookies, and the
new guidance, obsolete.
By Matt Klinger
The hype over Google Glass continues to build as the company
looks to expand its Explorers testing program and reportedly has
moored a barge in San Francisco bay to market the product.
Meanwhile, concern over the privacy implications of Glass do not appear to
have abated following Google's response to questions from nine foreign data privacy commissioners in
June. Articles discussing the privacy concerns Glass raises appeared in
the United Kingdom, Japan, Canada, India, and elsewhere in the last month alone.
While the
U.S. Federal Trade Commission did not join in the June letter, it is considering the privacy implications of wearable technology
like Google Glass, and is hosting a workshop
on the "Internet of things" next month.
GJIL would be happy
to try Glass out for itself and develop its own opinion. Here's to hoping
Google reads the Summit.
By Stephen Kozey
In a world where the majority of business transactions are
digital, it makes sense that trade in services would join the club. Surely
greater access to markets is good for business, but is the law, and
international law in particular, prepared to deal with the inevitable issues of
privacy, security, and digital piracy? If you want to find out more about the
impact of digital trade on business, entrepreneurs, and consumers, check out
the ASIL’s panel
discussion, “Traveling the Electronic Silk Road,” at 3:00 p.m. on Monday, October 7.
As a bonus, you can preview panelist Anupam Chander’s new book, “The
Electronic Silk Road,” for a taste of what’s to come on Monday.
By Matt Klinger
Data privacy officials from across the globe gathered in
Poland last week for the 35th Annual International Conference of Data
Protection and Privacy Commissioners. The conference attendees adopted
eight resolutions on various privacy issues including a call
for increased cross-border cooperation in data privacy
investigations and recommended safeguards for parties that engage in profiling.
Attendees also adopted a declaration addressing the "appification" of society. The declaration emphasizes that
app developers should only collect data necessary for their product's
performance and calls on operating system providers to offer more granular
privacy settings on mobile devices. The commissioners warned that if
their efforts to encourage better privacy practices regarding apps do not have
"sufficient effect," they "will be ready to enforce . . .
legislation in a global effort to reclaim user control."
By Matt Klinger
The Organization for Economic Cooperation and Development
(OECD) recently updated its Guidelines governing the Protection of Privacy and
Transborder Flows of Personal Data ("Revised Guidelines"). While the set of
eight principles established in the original guidelines published in 1980
remain intact, the Revised Guidelines introduce at least three new
concepts: (1) the importance of a coordinated national privacy strategy;
(2) the need for privacy management programs within organizations; and (3) data
breach security notification regimes.
In addition, the OECD has highlighted two themes that
run throughout the Revised Guidelines. First is a "focus on the
practical implementation of privacy protection through an approach grounded in
risk management." Second is the "need for greater efforts to
address the global dimension of privacy through improved
interoperability."
These revisions help modernize the guidelines to accommodate
vast changes in data generation and flows since 1980. They also serve,
however, to highlight the enduring nature of the OECD's data protection
principles.
By Elizabeth Gibson
Under
pressure from European regulators, Facebook stopped using facial recognition in
Europe last year and deleted existing data on European users. However, PC World and the Washington Post are reporting that the issue may be resurfacing.
Facebook
released proposed changes to its privacy policy last week, and German
regulators told PC World that they are concerned that the policy mentions facial
recognition. For now, Irish regulators said they have confirmed with Facebook that
the feature is still disabled in Europe.
Read
more at PC World and the Washington Post.


